FBI Disrupts Tools Linked to Chinese Cyber Operations
The Federal Bureau of Investigation and the US Department of Justice have intensified efforts to disrupt cyber operations linked to Chinese state sponsored hackers. In October 2026, authorities announced the seizure of tools allegedly used to scan vulnerable systems and conduct targeted cyber intrusions against critical infrastructure and other networks.
The latest operation highlights growing concerns about cyber threats targeting essential services, corporate networks and sensitive information. Furthermore, it reinforces the need for businesses to strengthen their cybersecurity defenses as sophisticated attackers combine automated scanning with hands on exploitation.
According to the US Department of Justice, the October 8 operation targeted two platforms known as Microscan and FishHub. Investigators allege that actors associated with China based Integrity Technology Group used the tools in activities linked to the hacking group known as Flax Typhoon.
Microscan and FishHub Target Vulnerable Networks
The FBI and Justice Department obtained court authorization to seize seven domains associated with the two platforms. The action was intended to prevent malicious actors from accessing infrastructure that supported their operations.
Microscan was associated with vulnerability scanning, while FishHub was linked to spear phishing and intrusion activity. These capabilities can help attackers identify weaknesses, target specific individuals and gain unauthorized access to organizational networks.
Moreover, the investigation connects the alleged activity to Integrity Technology Group, a Chinese company that US authorities say has links to the Chinese government. The allegations form part of a broader effort to counter cyber operations that threaten US infrastructure and other international targets.
The seizure represents a disruption of the tools used in the alleged campaign. However, taking down domains does not automatically eliminate every compromised device, exposed vulnerability or attacker operating through separate infrastructure.
A Broader Pattern of Chinese Linked Cyber Threats
The October operation follows other US government actions against cyber infrastructure allegedly connected to Chinese state sponsored groups.
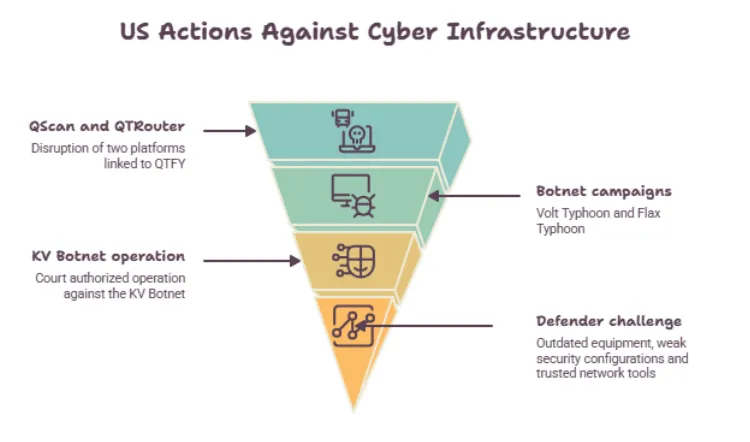
In August 2026, the FBI and Justice Department announced the disruption of two platforms called QScan and QTRouter. Authorities linked these tools to a group identified as QTFY and said they had been used to target US critical infrastructure and sensitive networks.
Earlier operations also targeted botnets associated with Volt Typhoon and Flax Typhoon. These campaigns demonstrated how attackers can use compromised internet connected devices to conceal their activities and maintain access to targeted networks.
In January 2024, the Justice Department announced a court authorized operation against the KV Botnet, which used compromised small office and home office routers to obscure the origin of hacking activity associated with Volt Typhoon.
These cases illustrate a continuing challenge for defenders. Attackers can exploit outdated equipment, weak security configurations and trusted network tools to move through systems while attempting to avoid detection.
Why Critical Infrastructure Remains at Risk
Critical infrastructure includes essential services such as energy, water, telecommunications and transportation. A successful intrusion into these environments could threaten service continuity, expose sensitive information or create opportunities for future disruption.
In a joint cybersecurity advisory, the FBI, the Cybersecurity and Infrastructure Security Agency and the National Security Agency warned that Volt Typhoon actors had sought persistent access to US critical infrastructure networks. The agencies assessed that this access could support disruptive or destructive operations during a major crisis or conflict.
The risk extends beyond government agencies and infrastructure operators. Private businesses often depend on shared suppliers, cloud platforms, remote access systems and third party service providers. Consequently, a weakness in one part of the supply chain can expose other organizations to security incidents.
Furthermore, attackers who gain access to corporate IT networks may attempt to reach operational technology systems that control physical equipment and industrial processes.
What Cybersecurity Experts and Authorities Recommend
US cybersecurity agencies have repeatedly urged organizations to reduce exposed vulnerabilities and improve their ability to identify suspicious activity.
In an FBI statement about earlier Volt Typhoon investigations, former FBI Director Christopher Wray described the operation as an effort to remove malware from compromised devices and prevent their reinfection. The statement underscored the importance of coordinated action between government investigators and private sector partners.
For organizations defending against similar threats, established security practices remain essential. These include promptly installing security updates, replacing unsupported routers and other network devices, enabling phishing resistant multifactor authentication and collecting logs centrally.
Additionally, security teams should monitor unusual account activity, restrict administrative privileges and review remote access connections. Regular incident response exercises can help employees and technical teams react more effectively when suspicious activity appears.
What Businesses Should Know
The latest disruption demonstrates that cybercriminals and state linked actors can rely on specialized tools and compromised infrastructure to target organizations at scale. However, businesses should not assume that law enforcement action alone will resolve their exposure.
Organizations should inventory internet facing systems, identify unsupported hardware and prioritize patches for actively exploited vulnerabilities. They should also assess third party access, review backup protection and confirm that security alerts reach the appropriate response teams.
For companies operating in finance, healthcare, telecommunications, manufacturing and other sensitive sectors, cybersecurity should remain a core operational priority rather than a purely technical responsibility.
The wider lesson for the IT industry is clear. Effective protection requires continuous monitoring, timely updates, employee awareness and cooperation between public authorities and private organizations.
For more Technology Insights and IT Industry News, visit infoproweekly.com
Follow infoproweekly.com for credible reporting on cybersecurity developments, business risks and emerging technology trends.